Hack your business before they do.
We’ve just opened the door to world-class offensive security for every business
Offensive security, unleashed
Using Aether, our own ~400B-parameter security AI extensively trained on nine years’ worth of real-world offensive-security data, we’ve made enterprise-grade penetration testing continuous, accessible and affordable.
Day Zero
Complete testing in hours, with actionable findings delivered the same day.
Always-hunting
Regular testing keeps pace as your attack surface changes and new threats emerge.
On-demand
Run a test whenever you need one. No scheduling, no waiting — just go.
Built around you.
AvalonX adapts its testing to your business, attack surface and unique risks.
Meet Artemis
Artemis is the platform that orchestrates Aether across a fleet of autonomous offensive-security agents. Each specialises in a different stage of an attack — working together, sharing what they learn and adapting their next move as the attack unfolds.
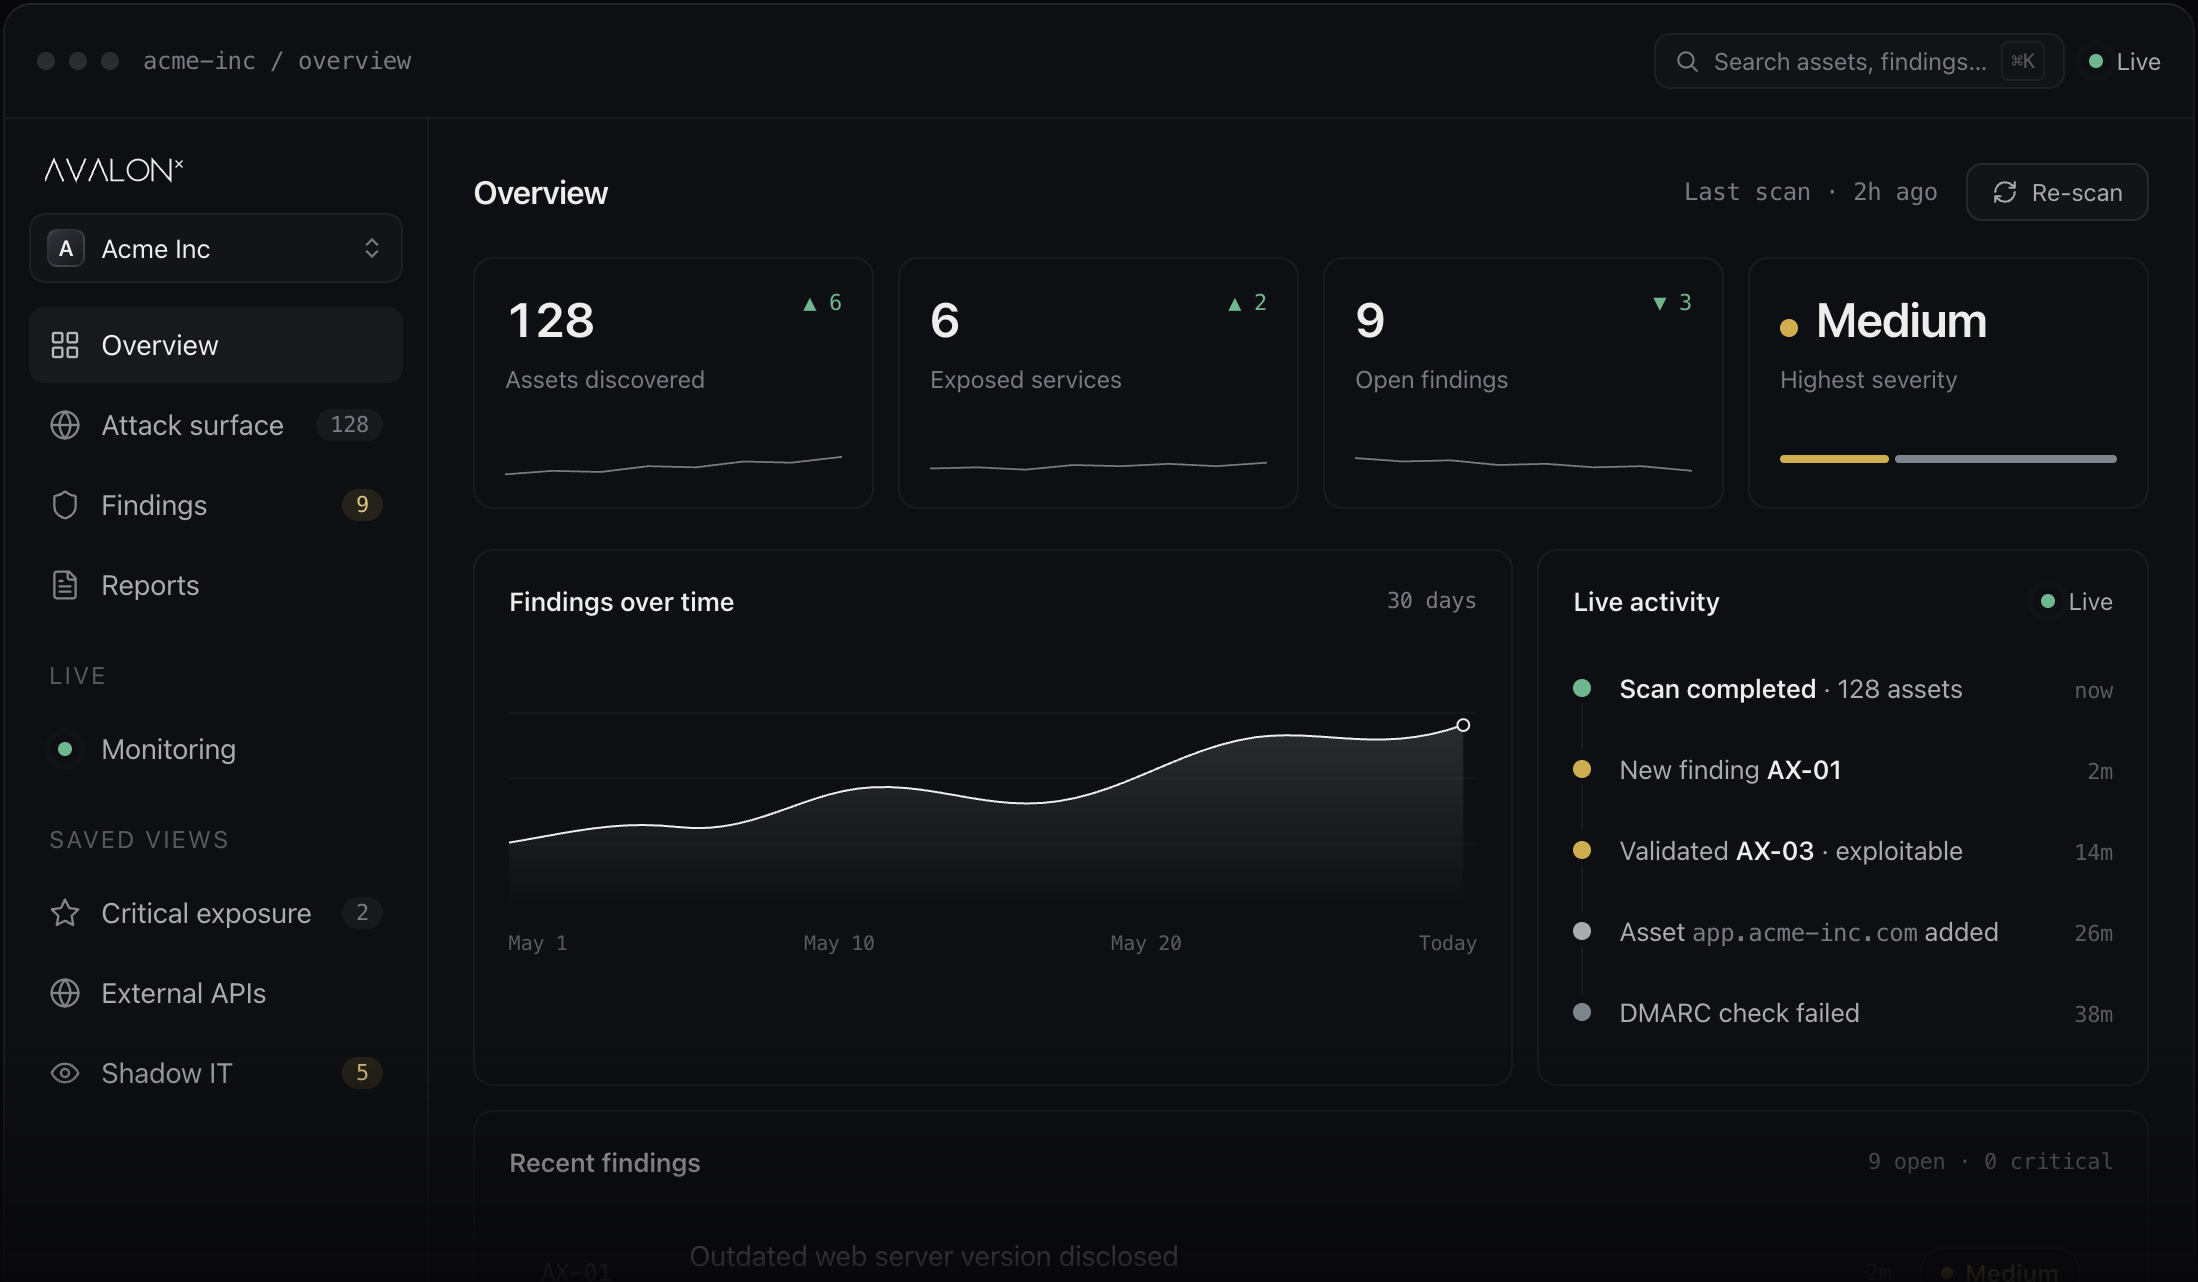
Turning intelligence into action.
Think. Act. Adapt.
Artemis doesn’t just follow a script. Its agents plan, execute against real security tools, evaluate the outcome and decide what to do next.
One mission. Many agents.
From reconnaissance and enumeration to exploitation, lateral movement and reporting, specialised agents work together and pass context from one stage to the next.
AI discovers. Humans verify.
When expert judgement is needed, Artemis escalates to our human penetration testers — combining autonomous speed with human expertise.
Attack.
Fix.
Repeat.
Add your domain, confirm your scope and you’re ready to go. No lengthy scoping calls or weeks of back-and-forth.
We test your business like an attacker would — finding vulnerabilities, connecting the dots and uncovering real paths to compromise.
Get clear, verified findings that show what matters, why it matters and what you need to do next.
Fix. Retest. Run another test whenever you want. Keep scanning 24/7. Your security keeps moving with your business.
Compliance. Covered.
AvalonX maps security findings to the controls and requirements relevant to your organisation, helping you maintain evidence for recognised security and compliance frameworks.
Continuous testing and evidence mapped to relevant Trust Services Criteria.
Security testing and evidence to support your information security management programme.
Support for penetration-testing requirements, including testing following significant changes.
Ongoing security testing to support risk analysis and security requirements.
More control.
Less complexity.
No security team needed
Get serious offensive-security capability without hiring specialists or building an in-house security function.
Complete risk visibility
See where you’re exposed, what could be exploited and which risks need your attention first.
On-going threat testing
Keep testing as your business changes, so new vulnerabilities don’t go unnoticed between annual tests.
Affordable enterprise protection
Access enterprise-grade testing through a subscription model designed to make it affordable for more businesses.
Audit-ready evidence
Maintain up-to-date testing evidence to support compliance requirements, audits and security reviews.
Clear, actionable reporting
Understand what’s wrong, why it matters and what to do next — without having to decode security jargon.